listen more to learn more.

Showing posts with label IT security. Show all posts

Wednesday, April 25, 2018

Portugal Joins NATO Cyber-Defence Centre

Portugal on Tuesday became the 21st country to join NATO's cyber defence centre, the Tallinn-based body said at a flag-raising ceremony. 

"We are facing adversaries who target our common values in cyberspace: freedom, truth, trust," centre director Merle Maigre said at the ceremony.

"To build resilience we need to come together. That is why I am glad to welcome Portugal as together we are stronger," she added. 

The centre was founded in 2008 in the capital of cyber-savvy Estonia, ranked as having one of the world's highest internet user rates, which itself had come under attack the previous year.

Estonia accused Russia, NATO's old Cold War foe, of being behind the attacks on its official sites and information networks.

At the centre, data experts from across Europe and the United States work to protect the information networks of the Western defence alliance's 29 countries. 

The centre's current members are Austria, Belgium, the Czech Republic, Estonia, Finland, France, Germany, Greece, Hungary, Italy, Latvia, Lithuania, the Netherlands, Poland, Portugal, Slovakia, Spain, Sweden, Turkey, the United Kingdom and the United States.
Australia, Norway and Japan have said they also plan to join.

New Tool Detects Evil Maid Attacks on Mac Laptops

A security researcher has developed a simple tool that helps Mac laptop owners detect unauthorized physical access to their device, also known as an evil maid attack, by monitoring its lid.

The free tool, named DoNotDisturb (DND), was created by Patrick Wardle, co-founder and chief research officer at enterprise macOS security company Digita Security.
Leaving a laptop unattended – for example, leaving it in the hotel room while traveling – puts the device at risk of evil maid attacks. An attacker who has physical access to the targeted device may steal data from it or install malicious software without leaving any obvious evidence behind.

The DND tool attempts to address this issue on Mac laptops by monitoring lid events. A majority of evil maid attacks require the attacker to open the device’s lid. However, there are some types of physical attacks that do not require opening the device’s lid, and the tool works based on the premise that the user closes the device’s lid when leaving it unattended.

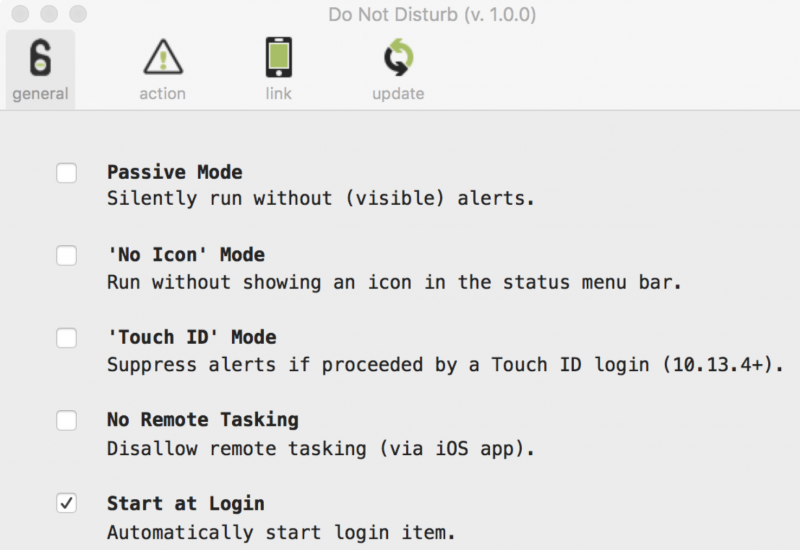
DND is a simple tool, but it does include some interesting features and options. Users can configure the app to start at login and run in passive mode, which means it will run silently without any visible alerts. The “No Icon” mode ensures that an icon is not displayed in the macOS/OS X menu bar, making the tool even stealthier.
DoNotDisturb - DND
The main tool installed on the monitored Mac laptop can be paired with an iOS application that allows the user to view alerts and respond. The iOS app can be used to dismiss an alert, take a picture of the individual using the monitored laptop, and remotely shut down the device. While the macOS tool is free, users have to pay a monthly or yearly subscription fee ($9.99 per year) to use the iOS companion for more than one week. The iOS app is optional, but users will not receive alerts and they cannot take any action remotely in case of an attack.

DND can be configured to take specific actions when the device’s lid is opened. For example, it can execute a script or a binary file, or it can start tracking the attacker’s activities, including new processes, new logins, and USB device insertions.

For users who want to keep DND active on their device at all times but do not want the app to trigger an alert whenever they open the laptop’s lid themselves, the tool can be configured to ignore lid events in specific cases. However, this setting requires a newer model Mac laptop that has a touch bar and is running macOS 10.13.4 or newer.

“When this mode is enabled, DND will ignore any lid open events if proceeded by a successful touch ID authentication event within 10 seconds. The idea is that this allows one to tell DND to trust (or ignore) a lid event that is a result of you (vs. somebody else) opening your laptop,” Wardle explained.

Wardle is well known on the Mac hacking scene thanks to the useful apps he has released and the vulnerabilities he has found in both Apple’s own code and third-party software.

Saturday, April 7, 2018

Facebook's Sandberg Says Other Cases of Data Misuse Possible

Facebook's Sandberg Says Other Cases of Data Misuse Possible

Sandberg, who joined Facebook in 2008 from Google, has been largely silent since the privacy scandal broke but she gave interviews on Thursday and Friday to National Public Radio and NBC's "Today Show."

"We know that we did not do enough to protect people's data," Sandberg told NPR. "I'm really sorry for that. Mark (Zuckerberg) is really sorry for that, and what we're doing now is taking really firm action."

"Safety and security is never done, it's an arms race," she said. "You build something, someone tries to abuse it."

"But the bigger (question) is, 'Should we have taken these steps years ago anyway?'" Sandberg said. "And the answer to that is yes.

"We really believed in social experiences, we really believed in protecting privacy, but we were way too idealistic," she said. 

"We did not think enough about the abuse cases and now we're taking really firm steps across the board."

Facebook has been scrambling for weeks in the face of the disclosure of the hijacking of private data by the British consulting group working for Donald Trump's 2016 presidential campaign.

'That's on us'

Sandberg said Facebook was first aware two and a half years ago that Cambridge Analytica had obtained user data from a researcher who put up a poll on Facebook.
"When we received word that this researcher gave the data to Cambridge Analytica, they assured us it was deleted," she said. "We did not follow up and confirm, and that's on us — and particularly once they were active in the election, we should have done that."
Sandberg was asked by the "Today Show" if other cases of misuse of user data could be expected.

"We're doing an investigation, we're going to do audits and yes, we think it's possible, that's why we're doing the audit," she said.
"That's why this week we shut down a number of use cases in other areas — in groups, in pages, in events — because those are other places where we haven't necessarily found problems, but we think that we should be more protective of people's data," she told NPR.
Sandberg said that starting Monday, the social network will put on top ot its news feed "a place where you can see all the apps you've shared your data with and a really easy way to delete them."

Sandberg said Facebook also should have been more proactive in dealing with Russian interference in the 2016 presidential election.
"That was something we should have caught, we should have known about," she told NPR. "We didn't. Now we've learned."

"We're going after fake accounts," she told the "Today Show." "A lot of it is politically motivated but even more is economically motivated."
Zuckerberg accepted responsibility this week for the failure to protect user data but maintained he was still the best person to lead the network of two billion users.
He is to appear before a US congressional panel next week to address privacy issues.
Facebook shares were down slightly in mid-morning trading in New York on Friday.

Thursday, April 5, 2018

Microsoft Adds New Security Features to Office 365

Microsoft Adds New Security Features to Office 365

Microsoft today announced new protections for Office 365 Home and Office 365 Personal subscribers, aimed at helping them recover files, protect data, and defend against malware.

Courtesy of the newly announced protections, Office 365 Home and Office 365 Personal users can now recover their files after a malicious attack like ransomware, Kirk Koenigsbauer, Corporate Vice President for Office at Microsoft, says.
The new functionality is available through a Files Restore option that has been long available for OneDrive for Business customers. The feature is now available for personal OneDrive accounts and is enabled for both work and personal files.
With the help of Files Restore, users can restore their entire OneDrive to a previous point in time within the last 30 days. The feature should prove highly useful in a variety of situations, ranging from an accidental mass delete to file corruption, ransomware encryption, or another catastrophic event.
To further protect users, Microsoft is bringing ransomware detection and recovery features to Office 365. This feature ensures that ransomware attacks are detected and also helps users restore their OneDrive to a point before files were compromised.
“If an attack is detected, you will be alerted through an email, mobile, or desktop notification and guided through a recovery process where you’ll find the date and time of attack preselected in Files Restore, making the process simple and easy to use. As these threats evolve, we are continuously improving detection capabilities to help keep you safe from the most advanced ransomware,” Koenigsbauer notes.
Microsoft is also retrofitting Office 365 with adding three new capabilities meant to help users keep their data secure and private when sending confidential or personal information online, regardless of whether via email or through sharing a link.
For starters, the software giant is allowing users to set and require a password to access a shared file or folder in OneDrive, thus preventing unauthorized access to their files, provided that the link is accidentally shared with a third-party.
Microsoft is also providing email encryption in Outlook.com, for an added layer of protection. Through end-to-end encryption of messages, the company aims at preventing hackers from intercepting and reading users’ communication.
“Encryption is particularly useful in cases where it is unclear what level of security your intended recipients’ email providers offer. Recipients receive a link to a trusted Office 365 webpage where they can choose to receive a one-time passcode or re-authenticate with a trusted provider before viewing the email,” Koenigsbauer says.
Recipients viewing encrypted emails in Outlook.com, the Outlook for iOS and Android app, or the Windows Mail app do not need to engage in extra steps to read and reply to messages. Outlook.com can also detect sensitive information like social security numbers when a new email is composed, and can provide a suggestion to send with encryption.
Additionally, users can now restrict email recipients from forwarding or copying emails sent from Outlook.com. Moreover, all Office documents attached to these emails are now encrypted even after downloading, meaning that, if they are forwarded to a third party, the recipient won’t be able to open the attachment.
Later this year, Office 365 Home and Office 365 Personal subscribers will also be able to take advantage of advanced link checking in Word, Excel, and PowerPoint. The functionality follows the advanced link checking and attachment scanning added to Outlook.com in October last year in an attempt to keep users protected from previously unseen viruses and phishing scams in real-time.
“Starting later this year, links you click in Word, Excel, and PowerPoint will also be checked in real-time to determine if the destination website is likely to download malware onto your computer or if it’s related to a phishing scam. If the link is suspicious, you will be redirected to a warning screen recommending you don’t access the site,” Koenigsbauer notes.

Sunday, December 11, 2016

Germany Accuses Russia of Hybrid Warfare

Russia has been accused of waging its own brand of cyber hybrid warfare against Germany, with specific focus on next year's elections. In particular, the APT28 (Fancy Bear) hacking group -- thought to be linked to the Russian government -- is accused of spreading propaganda and disinformation under the guise of 'hacktivists'.

The recent attack on Deutsche Telekom routers is thought by some experts to have emanated from Russia, but there is no proof. Last year's attack against the German parliament, and attacks against German politicians in August, are also blamed on Russia. Speaking earlier this week, Chancellor Angela Merkel commented, "Such cyber-attacks, or hybrid conflicts as they are known in Russian doctrine, are now part of daily life and we must learn to cope with them."

Now both the heads of the German foreign intelligence agency (BND), Bruno Kahl, and the domestic intelligence agency (BfV), Hans-Georg Maassen, have warned about increasing Russian cyber activity in Germany. 

Last week Kahl told the Süddeutsche Zeitung, "There are findings that cyber-attacks take place which have no other meaning than to create political uncertainty. There is a kind of pressure on public discourse and on democracy, which is unacceptable." He added that there are indications of Russian involvement. "Attribution to a state actor is technically difficult, but there is some evidence that it is at least tolerated or desired by the state."
Yesterday, however, a statement issued by the BfV was more forthright. "Since the start of the Ukraine crisis," it started, "we have seen a significant increase in Russian propaganda and disinformation campaigns in Germany." It warns of a broad spectrum of instruments and "an enormous use of financial resources on Russia's part" designed to strengthen extremist groups in order to shape political discourse in Germany.

The statement names APT28 as using a campaign that is often executed as 'false flags'. "This approach represents a previously unseen methodology in campaigns that are controlled by Russia." Note however, that many experts believe that the attack against French television company TV5  was also a 'false flag': in reality APT28 pretending to be ISIS.

The statement goes on to say, "Spear-phishing against political parties and parliamentary groups have increased dramatically. They are attributed to the APT28 campaign, which was also responsible for the DNC hack. APT28 successfully exfiltrated data from the German Bundestag in 2015."

Maassen describes the method and motivation behind the APT28 campaign. "Propaganda, disinformation, cyber-attacks, cyber espionage and cyber sabotage are part of hybrid threats against western democracies." He points to social networks as the new way for people to share and consume information, adding that it provides the perfect entry point for disinformation and campaigns designed to reshape public opinion.

He also warns of an "increase in cyber espionage within the political arena". Government officials, members of the Bundestag, and party workers all face a potential threat. "Stolen information could be used in the election campaign to discredit German politicians."
The political theory is that Russia will benefit from a weakened European Union -- already wounded by Brexit. By playing to European concerns over uncontrolled immigration and refugee support, and by fostering nationalism within individual member states -- in this instance Germany -- Russia will be able to weaken the existing European sanctions.
Russia denies involvement in hacking.

Yahoo Pays Out $10,000 Bounty for Critical Mail Flaw

A researcher has earned $10,000 for finding a critical Yahoo! Mail vulnerability that could have been exploited simply by getting the targeted user to open a specially crafted email.

Nearly one year ago, Jouko Pynnönen of Finland-based software company Klikki Oy discovered a stored cross-site scripting (XSS) vulnerability in the web version of the Yahoo! Mail service that could have allowed an attacker to execute malicious JavaScript code hidden in emails.

The researcher said the flaw could have been used to forward the victim’s emails, change their account settings and even create an email worm that attached itself to all outgoing emails.

The vulnerability, which earned Pynnönen $10,000, existed due to Yahoo’s failure to properly sanitize code in HTML emails.

The expert recently decided to take another look at Yahoo’s Mail service and discovered a similar flaw, but this time it was related to code inserted when certain type of content is attached to an email.

The “Share files from cloud providers" attachment option allows users to attach files from their cloud storage accounts, such as Dropbox or Google Drive. While analyzing the code inserted into an email when this option was used, Pynnonen noticed some HTML attributes named data-* (e.g. data-url, data-category, data-embed-url). Further analysis showed that these attributes are also used when a YouTube video is added to an email.

The researcher found a way to abuse these attributes in YouTube video attachments to get arbitrary JavaScript code executed. There was no need for the user to click on a link or open an attachment – the code would get executed as soon as the email was opened.
Similar to the flaw discovered one year ago, this security hole could have been exploited to steal a user’s emails and create a worm that spreads by attaching itself to outgoing emails, the expert said.

Pynnönen told SecurityWeek that he did not get a chance to test the attack method using the Google Drive and Dropbox attachment options. Yahoo was informed about the vulnerability on November 12 and fixed it by the end of November.

Yahoo awarded the expert a $10,000 bounty for the flaw. The company reported in May that it had paid out more than $1.6 million since the launch of its public bug bounty program in 2013.

Russia Says Thwarted Fresh Cyber Attacks on Major Banks

Russia's telecom operator on Friday said that it had blocked a series of cyber attacks on the country's leading banks this week, the latest to target the country's financial sector.

Rostelecom said in a statement that it "successfully thwarted DDoS (distributed denial of service) on the five biggest banks and financial organisations in Russia" on December 5.
"The most sustained attack lasted more than two hours," it said.

Russia's FSB security service last week said it had uncovered plans by foreign intelligence services to carry out massive cyber attacks targeting the country's financial system from December 5.

State-controlled Russian bank VTB said Monday that its websites had been hit by a cyber attack but insisted its systems were still working "as normal".

The FSB did not say which countries' secret services were involved in the latest plot against Russian banks but alleged the attacks would use servers and "command centres" located in the Netherlands belonging to Ukrainian hosting company, BlazingFast.

Russia has been embroiled in a hacking scandal with the US over allegations from Washington that Moscow was behind the theft and leaking of documents online during the run-up to the US presidential election aimed at influencing the outcome.

Vice President Joe Biden warned that the US would respond to the suspected Russian hacking "at the time of our choosing and under the circumstances that have the greatest impact".

The latest attacks comes after Moscow-based security giant Kaspersky said in November that a massive DDoS cyber attack had hit at least five of Russia's largest banks.

DDoS attacks involve flooding websites with more traffic than they can handle, making them difficult to access or taking them offline entirely.

Kaspersky said those attacks used devices located in 30 countries including the United States.

Thursday, December 8, 2016

Experts Propose Cybersecurity Strategy for Nuclear Facilities

Institutionalizing cybersecurity, reducing complexity, active defenses and transformative research should be a priority in reducing the risk of damaging cyberattacks at nuclear facilities, according to the Nuclear Threat Initiative (NTI).

While the Stuxnet attacks aimed at Iran are the most well-known, nuclear facilities in Germany and South Korea have also been hit by cyberattacks. European Union officials have also raised concerns about the possibility of attacks against Belgium’s nuclear plants.

Reports published in the past months warned that countries are not prepared to handle attacks targeting their nuclear facilities, and the nuclear industry still underestimates cyber security risk.

A report published on Wednesday by the NTI provides a set of recommendations for improving cyber security at nuclear facilities based on a 12-month analysis conducted by an international group of technical and operational experts.

One of the most important priorities involves institutionalizing cybersecurity. Specifically, nuclear facilities should learn from their safety and physical security programs and integrate these practices into their cybersecurity programs.
Nuclear Cyber Security
Governments and regulators can also contribute by prioritizing the development and implementation of regulatory frameworks and by attracting skilled people into this field. International organizations have been advised to provide guidance and training, and support cooperation and an increased focus on cybersecurity through dialog and best practices.
Another priority should be active defenses. Experts pointed out that a determined adversary will likely be capable of breaching the systems of a nuclear facility and organizations must be prepared to efficiently respond to such incidents.
Sharing threat information, incident response exercises, more resources from governments, and the development of active defense capabilities are some of the recommendations for addressing this issue, but experts admit that it’s not an easy task due to the global shortage of technical experts.

Reducing the complexity of digital systems should also be a priority for nuclear facilities. Experts recommend minimizing the complexity of digital systems and even replacing them with non-digital or secure-by-design products.

Finally, the NTI recommends conducting transformative research with the goal of developing hard-to-hack systems for critical applications. The list of actions includes governments investing in transformative research, the nuclear industry supporting the cybersecurity efforts of relevant organizations, and international organizations encouraging creativity for mitigating cyber threats.

“Today’s defenses are no longer adequate, and a fresh look at how to best protect nuclear facilities from cyberattack is needed,” experts wrote in the NTI report. “The threat is too great, and the potential consequences are too high, to remain comfortable with the status quo.”

Wednesday, December 7, 2016

Windows 10 Creators Update Brings New Security Capabilities

Microsoft Introduces New Enterprise Security Capabilities With Windows 10 Creators Update

Microsoft announced on Tuesday that the Windows 10 Creators Update, which it plans on releasing free of charge next spring, will include several new security capabilities designed to help IT teams protect their networks and devices.

In its initial announcement on the Windows 10 Creators Update, Microsoft focused on the creativity aspect, including productivity and gaming. However, the tech giant revealed on Tuesday that the update will also include significant security enhancements.

One of these improvements will make it easier for IT teams to monitor and act on security events by centralizing them in the Windows Security Center, a portal first released in the Windows 10 Anniversary Update. By linking the Security Center to Office 365 Advanced Threat Protection (ATP), administrators will be able to track a threat across endpoints and email (e.g. determine which users received a malicious email).

In Creators Update, the Windows Defender ATP will also provide enhanced detection, intelligence and remediation capabilities. ATP sensors will be expanded to detect kernel-level exploits and threats that persist only in memory. Once a threat has been identified, defenders will be able to select from a wider range of remediation actions, such as isolating machines, collecting forensics, quarantining files, and killing processes.
As for intelligence, FireEye recently announced that iSIGHT has become available to Microsoft enterprise users through Windows Defender ATP. Starting with Creators Update, users will be able to feed their own intel into the Security Center.

Microsoft said the new Windows 10 release will also provide an enhanced Windows Analytics dashboard that will help administrators manage their devices better, and a mobile application management feature designed to protect data on personal devices without the need to enroll them in an MDM solution.

Up until now, users who installed Windows 7 using a legacy BIOS and wanted to take advantage of new Windows 10 security features that required UEFI (e.g. Device Guard) had to manually configure the firmware. Creators Update will include a simple conversion tool that will automate the task.

Monday, December 5, 2016

Saudi Aviation Agency Downplays Impact of Shamoon Attack

Saudi Arabia’s General Authority of Civil Aviation (GACA) has confirmed that several government agencies, including its own systems, have been hit by the recent Shamoon 2.0 attacks, but downplayed the impact of the incident.

Shamoon, aka Disttrack, is a disk-wiping malware that became widely known in 2012, when it damaged 35,000 computers belonging to national petroleum and natural gas company Saudi Aramco.

Security firms noticed recently that a new version of the malware, dubbed Shamoon 2.0, has been used in attacks aimed at Arab states of the Persian Gulf, but little is known about the victims.

Bloomberg reported last week that several government agencies were targeted and named GACA. Sources told the publication that the attackers erased critical data and brought operations to a halt for several days. Thousands of computers were reportedly “destroyed” at the agency, but only office administration systems were affected.
In a statement published on its website, the aviation agency said the attack targeted various sectors, including the country’s transportation sector. GACA has confirmed that its systems were targeted, but claims its website and critical aviation systems were not impacted thanks to “security measures.”

According to the organization, the hackers did not breach air navigation systems or any major airport networks, including HR, financial, aviation permit and security badge, and airport support and operations systems.

“From the beginning of the attack in the past few days, GACA have noticed its impact on some of employees desktop pcs and their official emails, requiring us to immediately implement some necessary measures to deal with such incidents, where a complete isolation of the infected devices from the main network,” the agency stated.

“Work have already started to restore the infected data in a secure fashion. Efforts to provide employees with virus free and sound equipment was implemented immediately to enable them to carry on their workloads. Service was restored to the affected systems after a temporary injunction on the device was implemented as a precautionary measure for some time,” it added.

Shamoon 2.0 is similar to the original malware and the attack method suggests that the new campaign was carried out by the same threat actor that breached Saudi Aramco in 2012. A group calling itself the “Cutting Sword of Justice” took credit for the 2012 attack, but many believe the Iranian government was behind the operation.

State-owned Russian Bank VTB Says Sites Hit by Cyberattack

State-controlled Russian bank VTB said Monday that its websites had been hit by a cyberattack but insisted its systems were still working "as normal".

"A DDoS (distributed denial of service) attack was carried out against VTB Group internet sites," Russia's second largest bank said in a statement carried by Russian news agencies.
"Our IT infrastructure is working as normal and the bank's clients are not experiencing any difficulties."

Russia on Friday said it had uncovered plans by foreign intelligence services to carry out massive cyberattacks this month targeting the country's financial system.

The FSB security service said in a statement that it had received information on "plans by foreign secret services to carry out large-scale cyberattacks from December 5".

The FSB did not say which countries' secret services were involved in the latest plot against Russian banks but alleged the attacks would use servers and "command centres" located in the Netherlands belonging to Ukrainian hosting company BlazingFast.

Russia has been embroiled in a hacking scandal with the US over allegations from Washington that Moscow was behind the theft and leaking of documents online during the run-up to the US presidential election aimed at influencing the outcome.

Vice President Joe Biden warned that the US would respond to the suspected Russian hacking "at the time of our choosing and under the circumstances that have the greatest impact".

The latest attack on VTB comes after Moscow-based security giant Kaspersky said in November that a massive DDoS cyberattack had hit at least five of Russia's largest banks.
DDoS attacks involve flooding websites with more traffic than they can handle, making them difficult to access or taking them offline entirely.

Kaspersky said those attacks used devices located in 30 countries including the United States.

Russia's largest lender, state-controlled Sberbank, acknowledged it had been hacked but said its operations had not been interrupted. 

Saturday, December 3, 2016

50 Million Potentially Impacted by AirDroid Vulnerabilities

Vulnerabilities in the Android remote management tool AirDroid potentially impact over 50 million devices, security researchers at Zimperium zLabs warn.

The application has seen between 10 and 50 million downloads through the official Google Play software portal, but the security firm says that its device base is larger than that. According to Zimperium (the security firm that discovered the Stagefright flaw in Android), vulnerabilities in AirDroid allow an attacker to exploit built-in features and use them against the application’s users.

The issue, the security researchers say, is that AirDroid uses insecure communication channels, which means that the application’s millions of users are exposed to Man-in-the-Middle (MitM) attacks and other types of nefarious acts. Information leakage is also possible, along with remote hijacking of update APKs, which could result in remote code execution.

While analyzing AirDroid, the security researchers discovered that the communication channels employed to send authentication data to the statistics server are insecure. While the requests are encrypted with the Data Encryption Standard (DES) symmetric-key block cipher in Electronic Codebook (ECB) mode, the encryption key is hardcoded inside the application, meaning that the attacker knows it.

Armed with these details, an actor on the same network with the target device could execute MitM attacks to grab authentication credentials from the very first HTTP request the application performs, and can then impersonate the user for further requests, Zimperium’s Simone Margaritelli explains.

“This HTTP request can be decrypted at runtime using the 890jklms key hardcoded inside the application and the authentication fields parsed from the resulting JSON. Having this information, the attacker can now impersonate the victim’s device and perform various HTTP or HTTPS requests on its behalf to the AirDroid API endpoints,” the researcher notes.

An attacker could craft a payload encrypted in DES with the same exact key to trick the server into spewing user information, which will result in the email and password hash being exposed.

What’s more, an attacker performing MitM could also redirect HTTP traffic to a malicious transparent proxy, thus being able to modify the response for the /phone/vncupgraderequest, which the application normally uses to check for addons updates. Thus, by injecting a fake update, the actor could execute malicious code remotely on the compromised device, because AirDroid notifies the user about an update, downloads the RCE.apk package, and might even prompt the user to install it.
Zimperium notes that most of the AirDroid’s functionalities are carried out using secure HTTPS API endpoints, but insecure channels are used for specific tasks, such as the sending of statistics to a remote server. For security, the app relies on DES encrypted JSON payloads for this type of communication, but the use of a hardcoded key (determined to be 890jklms) nullifies the security measure.

To resolve these issues, researchers say, the application should use only secure communication channels (HTTPS), should verify the remote public key (key pinning) to avoid SSL MitM, should use safe key exchange mechanisms, and should leverage and verify digital signatures for update files.

The company also explains that these issues were discovered in May this year, when the developer was notified. However, although two updates were released this week in the form of AirDroid 4.0.0 and AirDroid 4.0.1, the application continues to be vulnerable, putting tens of millions of users at risk.

To stay protected, Zimperium says, users are advised to uninstall or disable AirDroid until a fix is available. They should also install and maintain an anti-malware solution on their Android devices.

Thursday, December 1, 2016

Bug Allows Activation Lock Bypass on iPhone, iPad

Researchers have found a bug that can be used to bypass Apple’s Activation Lock feature and gain access to the homescreen of locked iPhones and iPads running the latest version of iOS.

There seem to be at least two variations of the vulnerability – one of them works on iOS 10.1 and the second has also been reproduced on the latest 10.1.1 version of Apple’s mobile operating system.

The Find My iPhone service allows users to activate Lost Mode on their iPhone, iPad or iPod if the device is lost or stolen. When Lost Mode is used, it automatically enables Activation Lock, a feature that prevents reactivation of the device without the legitimate owner’s permission.

When a locked device is started, users are prompted to connect to a Wi-Fi network. If the “Other Network” option is selected, the user must enter the name of the network and choose a security protocol (e.g. WEP, WPA2, etc.). Depending on which protocol is selected, a username and/or a password must also be entered.

The problem, as researchers discovered, is that there is no limitation on the number of characters that can be entered into the name, username and password fields. By entering very long strings into these fields, an attacker can trigger a crash that exposes the device’s homescreen.

The crash can be triggered using at least two methods. The first involves Apple’s iPad smart cases, which cause the device to wake or sleep when the case is opened or closed.
The flaw was first discovered by India-based security enthusiast Hemant Joseph, who started analyzing the Activation Lock feature after purchasing a locked iPad from eBay. He managed to trigger the crash that gave him access to the homescreen by closing and opening the smart case.

This method worked on iOS 10.1, but the bug was addressed in iOS 10.1.1, which Apple released on October 31.

Researchers at Vulnerability Lab also analyzed the issue and discovered that it can be reproduced on iOS 10.1.1 using the screen rotation feature and Night Shift mode. In the video published by Vulnerability Lab, the homescreen is only visible for a second, but the company’s founder, Benjamin Kunz-Mejri, told SecurityWeek that access can be maintained by quickly pressing the power button.

The videos published by Vulnerability Lab and Joseph show how the bug is triggered on an iPad, but Kunz-Mejri said the bug affects iPhones as well.

Popular Posts

Contact

anmol3886@gmail.com